DepSentinel
Quiet signalBlock malicious dependencies before they reach your machine
Launched 24d ago
Signal
20
Velocity
0
What this means
50%Vote pace is below typical for Developer Infrastructure.
Running at 50% of comparable launches.
+63%Launching in a 63% WoW growing category.
Security had 39 launches this week vs 24 last.
14Founder Conviction Index: 14 — low signal.
Few of the conviction sub-signals (reputation, velocity, buyer-intent, tagline clarity) are firing yet.
Prediction
Top-5 finish probability
3%
today
Projected end-of-day votes
3range 2–4
Trajectory
stable
Vote pace holding steady.
Speed vs peers
0.5×
130 Developer Infrastructure launches
About
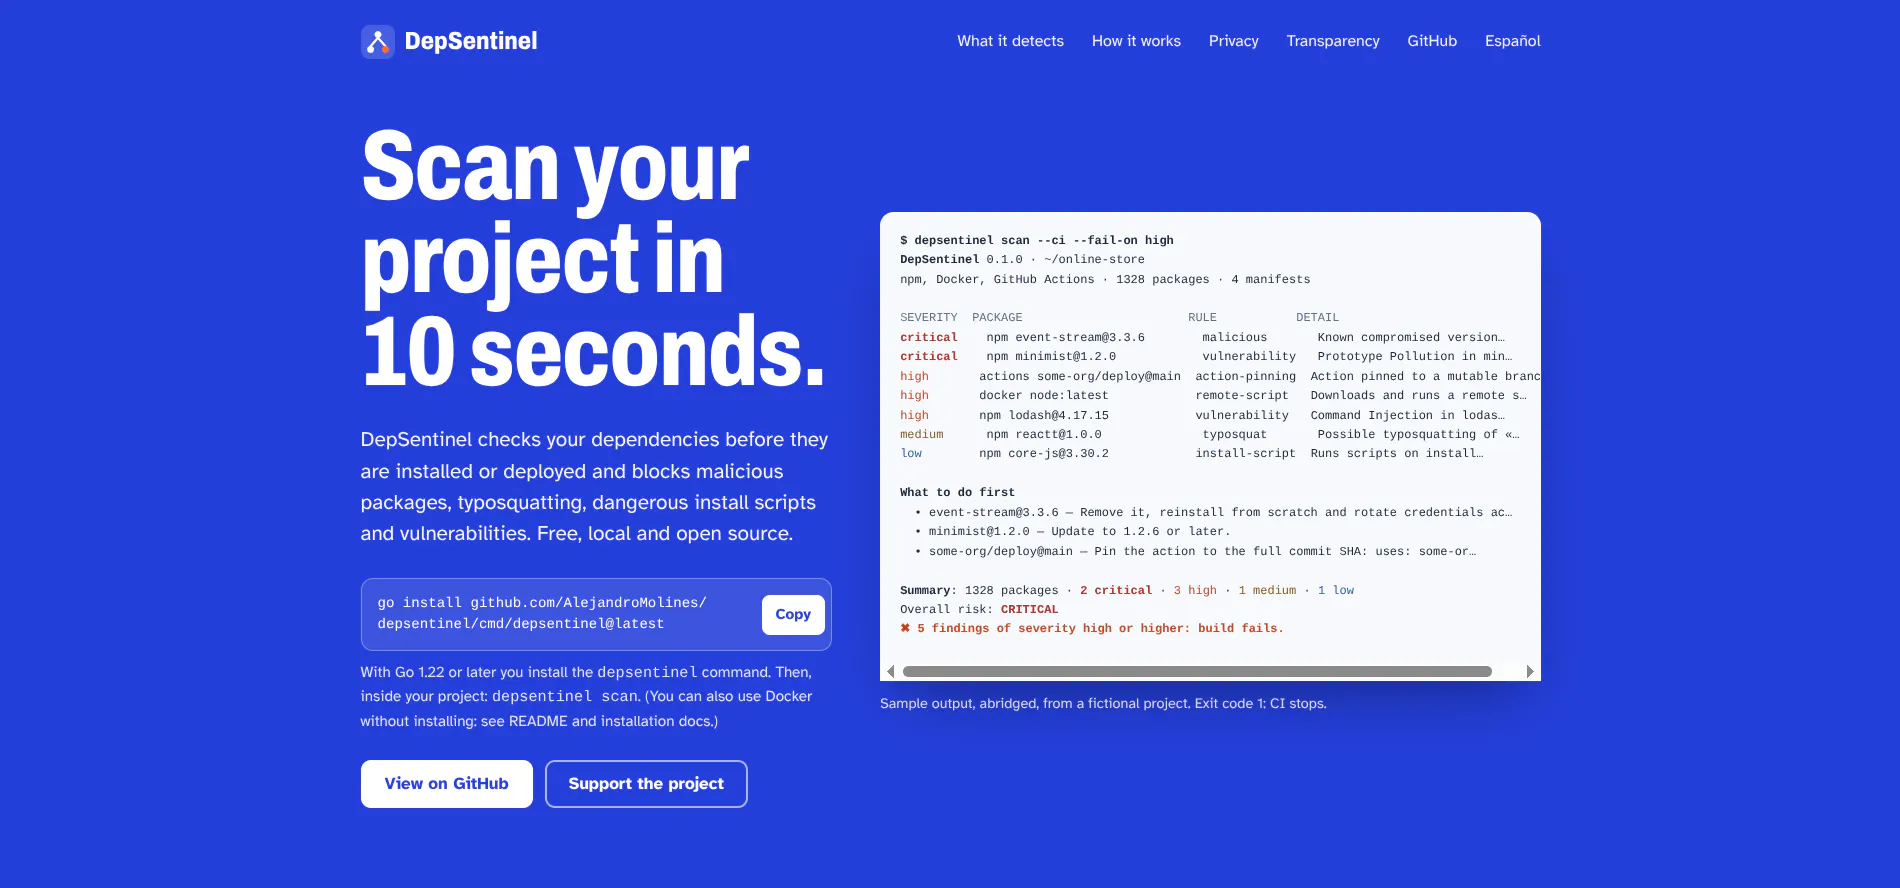
Blocks malicious packages, typosquatting and vulnerable dependencies before they reach your machine or production. Scans npm, PyPI, Go, Docker and GitHub Actions in seconds, 100% local, no account, no telemetry. Free and open source (MIT). Runs in CI and comments on pull requests. Includes a preventive guard: `depsentinel guard npm install` generates the lockfile with --ignore-scripts, scans it, and only then installs.
AI Summary
DepSentinel is an open-source security tool that scans and blocks malicious packages and vulnerable dependencies in npm, PyPI, Go, Docker, and GitHub Actions. It operates locally without requiring an account or telemetry, and integrates with CI to comment on pull requests.
Attention & discussion velocity
Performance
Velocity0
Vote pace vs average
Momentum0
Sustained over 6h
Virality0
Spread × engagement
Engagement—
not measured
Signal sources
2 of 6 active- Launch tracking4 readings since we picked it up
- AI analysisDeveloper Infrastructure
- Comment intelligencethread not yet analysed
- Outside discussionnot checked — domain is a storefront or shared
- Revenue signalsno match on this domain
- Editorial scoringbelow the signal threshold for this pass
A source that found nothing is a measurement. A source that has not run is a gap. Neither means the launch lacks the thing.